Last updated November 9, 2026. This is a developing story. WP Engine still hasn’t published an explanation. We added what its status page showed during those two days and how our fixes went, and we’ll update this post if WP Engine says more.
Between the evening of November 5 and the afternoon of November 6, 2026, WP Engine rewrote the wp-config.php file on every WP Engine site we manage. On the sites we could test, the WordPress salts in that file changed. That broke FluentSMTP, the plugin many WordPress sites use to send email, without showing anyone an error. Contact forms still say “thank you”, but the notification email never reaches your inbox. If your site is on WP Engine, check your email today. If something looks wrong, contact us right away and we’ll fix it with you.
On WP Engine, and your emails or plugins stopped working?
Contact us as soon as you can. We’ve already fixed this on a client’s live site, and it took under an hour and a half from first failure to email sending again.
What happened on WP Engine on November 5 and 6?
WP Engine rotated customer credentials and rewrote every site’s wp-config.php file. Plugins that use the file’s security keys for encryption stopped working.
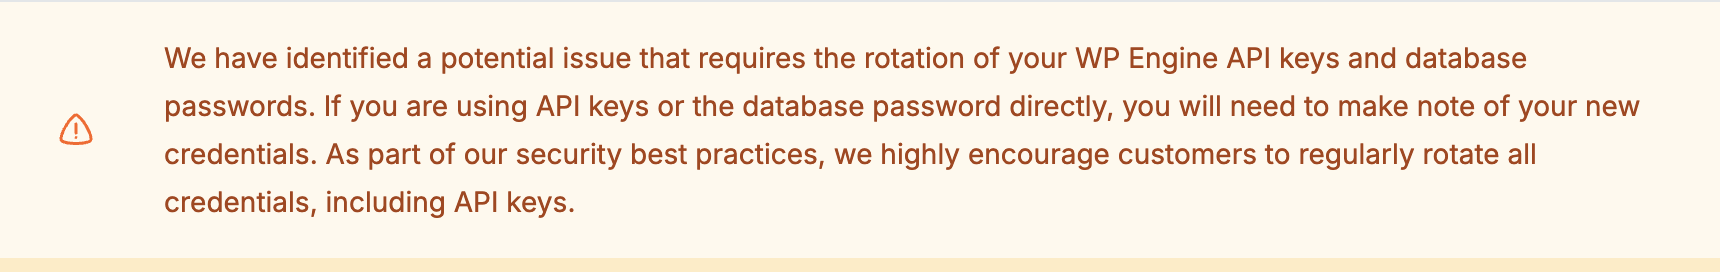
WP Engine customers are now seeing this notice at the top of the User Portal, asking them to take note of new API keys and database passwords:
On our end, every one of the 54 WP Engine installs we manage had its wp-config.php rewritten between 6:51 PM Eastern on November 5 and 1:14 PM Eastern on November 6. It happened in three waves, and on some installs the changes landed about 12 seconds apart, one site after the next. No other file changed in that window. On WP Engine, WordPress itself can’t write .php files, so a plugin or a wp-admin user couldn’t have done this. It came from the platform.
The notice mentions API keys and database passwords. It doesn’t mention the WordPress salts. But on nine sites, a password that a plugin had saved in encrypted form stopped decrypting at the same moment, and the only thing that explains that is new salts.
WP Engine’s status page doesn’t mention salts or credentials either, but it shows a busy two days. SSH access had problems from 8 PM Eastern on November 5 until the afternoon of November 7. A User Portal issue “impacting jobs” was posted at 2:19 PM on November 6. Then WP Engine ran two rounds of “Percona Emergency Maintenance” across all regions, from 6:30 PM on November 6 to 5:05 AM on November 7, and warned that sites could see intermittent downtime. Percona is a version of MySQL, the database WordPress runs on. None of those notices explain the wp-config.php changes, and as of November 9 we haven’t found a customer email or public statement that does.
What are WordPress salts?
WordPress salts are random strings in wp-config.php that secure your login cookies. Some plugins also use them as encryption keys for passwords they store.
Every WordPress site has eight of them: four keys (AUTH_KEY, SECURE_AUTH_KEY, LOGGED_IN_KEY, NONCE_KEY) and four salts with matching names. People usually call the whole set “the salts”. The WordPress developer handbook says you can change them “at any point in time to invalidate all existing cookies”, and that “all users will have to login again” when you do. So when the salts change, logging everyone out is expected. Nobody plans for the side effect: any plugin that used the old salts to lock away a password can’t unlock it anymore.
Why did FluentSMTP stop sending email?
FluentSMTP encrypts your saved email password with two of the WordPress salts. New salts mean it can’t read the password, so the mail server rejects the login.
In FluentSMTP’s code, the encryption key comes from LOGGED_IN_KEY and the salt from LOGGED_IN_SALT, unless the site defines its own. When WP Engine replaced those values, FluentSMTP kept decrypting the stored password with the new keys and got garbage back. It sends that garbage to the mail service, the login fails, and the email log shows SMTP Error: Could not authenticate.
Your SMTP password didn’t change. The key that unlocks it did. On Round-a-Bout, one of the sites we manage, the encrypted password in WP Engine’s own backup from before the change is byte-for-byte the same as the one that started failing.
In Eastern time, the last good email went out at 3:16 PM on November 5. WP Engine rewrote the site’s wp-config.php at 12:25 PM on November 6. The next email the site tried to send, at 1:25 PM, was a contact form lead notification, and it never arrived. We had email sending again at 2:42 PM and confirmed it with a real message. Nobody on the site saw an error. The form worked, the visitor saw the thank-you message, and the lead just didn’t show up in anyone’s inbox.
FluentSMTP’s developers know salt changes cause this. A proposed fix that cited salt rotation “by some hosts” was closed on November 4, two days before this happened. The maintainers’ advice is to pin your own encryption key in wp-config.php. We cover that below.
Which other plugins can break when WordPress salts change?
Any plugin that encrypts stored passwords, API keys or login tokens with the WordPress salts. Email plugins and Google connections are the most common.
- FluentSMTP (password or API key connections): broken on eight of the WP Engine sites we manage. Each one fails on its next email until someone saves the credentials again.
- FluentSMTP Gmail or Outlook connections: the saved login token is encrypted the same way. Ours stopped working and needs to be re-authorized with Google.
- Site Kit by Google: its encryption code also uses
LOGGED_IN_KEYandLOGGED_IN_SALT. If Site Kit shows you as disconnected, set it up again. - Anything that reads the WP Engine database password or API keys: deploy scripts, backup tools and reporting apps that connect with those credentials need the new ones from your WP Engine portal. The notice above says so directly.
- Logged-in users: everyone, including your customers, was logged out and has to sign in again. That’s normal after a salt change.
Settings saved as plain constants in wp-config.php came through fine for us. On the one site where the email service key lived in wp-config.php instead of the database, that connection kept working. We haven’t tested every plugin, so if your site uses WP Mail SMTP, Post SMTP or another mail plugin, send yourself a test email instead of assuming it’s fine.
How do I check if my WP Engine site is affected?
Send a test email from your mail plugin, then look at its email log for failures since November 5. A “Could not authenticate” error confirms it.
Seeing WordPress emails not sending on a WP Engine site since November 5? Rule this out first:
- In wp-admin, open FluentSMTP and send a test email to an address you can check.
- Open FluentSMTP’s email log and filter for failed emails. Anything after November 5 with
Could not authenticateis this problem. - Fill out your own contact form and make sure the notification arrives.
- Open Site Kit, if you use it, and see whether it still shows your Analytics and Search Console data.
- If you have more than one site on WP Engine, check every one. The change hit every install we manage, not just one.
How do I fix FluentSMTP after the WordPress salts changed?
Re-enter the same SMTP password or API key in FluentSMTP and save it. That encrypts it again with the new salts. Then send a test email.
- Go to FluentSMTP, then Settings, and edit the connection that’s failing.
- Paste your SMTP password or API key in plain text and save. Use the real password from your email provider. If you paste in a value that’s already encrypted, it gets encrypted twice and still fails.
- For Gmail or Outlook connections, click through the authorization again instead.
- Send a test email and confirm it shows as sent in the log.
- Go back through the failed emails since November 5. FluentSMTP lets you retry failed emails from the log. Most form plugins also save each submission in wp-admin, so check your form entries for leads that came in while email was down.
Don’t skip that last step: every missed notification is someone who filled out your form and is still waiting to hear back.
That’s what we did on our own sites, and all nine affected sites we manage are sending email again. On most of them, re-saving the email password was the whole fix, Round-a-Bout included. The one Gmail connection had to be reconnected instead. On the sites we fixed on November 6, we also switched on FluentSMTP’s failure alerts so a silent failure reaches us right away.
How do I keep WordPress salt changes from breaking email again?
Give FluentSMTP its own encryption key in wp-config.php, turn on its failure alerts, and test your forms after any hosting change.
- Pin the encryption key. FluentSMTP checks for
FLUENTMAIL_ENCRYPT_KEYandFLUENTMAIL_ENCRYPT_SALTconstants before it falls back to the WordPress salts, which is what its maintainers recommend for sites whose salts may change. Add both as long random strings, then re-save your SMTP password so it’s encrypted with them. On WP Engine you editwp-config.phpover SFTP or SSH, because WordPress can’t edit it from inside. - Turn on failure alerts. FluentSMTP can message you on Slack, Discord, Telegram or Pushover when an email fails. On Round-a-Bout, the site’s own health check said everything was fine the whole time, because nothing was watching outgoing mail.
- Test after any hosting change. Migrations, security sweeps and credential rotations all touch
wp-config.php. A two-minute form test afterwards catches this.
We checked every WP Engine site we manage the same day this happened. If you’d like someone keeping an eye on yours, take a look at our website hosting and maintenance plans.
Frequently asked questions
Did WP Engine change the WordPress salts on every site?
WP Engine rewrote wp-config.php on all 54 WP Engine installs we manage between November 5 and 6, 2026. On every site where a plugin's encrypted password stopped working, the salts had changed. WP Engine hasn't published an explanation yet.
Will changing WordPress salts log everyone out?
Yes. WordPress uses the salts to secure login cookies, so new salts end every logged-in session. Admins, editors and customers all have to log in again. That part is normal and harmless.
Do I need a new SMTP password after the salts changed?
No. Your password with your email provider still works. FluentSMTP just can't read its saved copy. Paste the same password or API key into FluentSMTP, save it, and send a test email.
Are the contact form leads that failed lost?
The notification emails weren't delivered, but FluentSMTP logs failed emails and lets you retry them. Most form plugins also save every submission in wp-admin, so check your form entries for anything since November 5.
How do I stop FluentSMTP breaking when WordPress salts change?
Define FLUENTMAIL_ENCRYPT_KEY and FLUENTMAIL_ENCRYPT_SALT in wp-config.php with long random values, then re-save your SMTP password. FluentSMTP uses those instead of the WordPress salts, so a future salt change won't affect it.
What does WP Engine's credential rotation notice mean?
WP Engine says it found a potential issue and rotated customers' API keys and database passwords. If a script, deploy tool or app uses those credentials directly, copy the new ones from your WP Engine portal.
Need help with your WP Engine site?
If your site is on WP Engine and your forms, email or connected plugins stopped working on November 5 or 6, contact us as soon as you can. We’ll find what broke, get it working again and track down any leads you missed. Contact us here or call (919) 444-2005.
We also covered another recent WordPress problem worth checking: the WordPress core flaw attackers are using during updates.